We co-led the €2M pre-seed round in Gardera, a Stockholm startup building the Nordics’ first product security company.
Software teams have never been short on security alerts. Scanners flag hundreds of findings, most of them false positives, and the few that matter hide in a backlog because nobody finds them from the noise to prove and fix them. That was manageable when humans wrote the code and humans tried to hack your software. It stops being manageable when agents write ten times as much code, and most of it ships without human reading and proving the pull requests.
Gardera is built for the requirements of today’s AI era. Founded in 2025 by Marcus Modin, Patrik Nordlén and Shehzaad Saifulla, the company runs an AI-native AppSec platform with its own autonomous security engineer. It reads the code, attacks the customer’s running application to prove what is exploitable, ignores what is not, and opens a pull request with the fix. Developers stay in the loop through tools they already use, with no new pipeline step to adopt.
The round was co-led by Vendep and DIG Ventures, with participation from Greens Ventures, Further Than Capital, Sequence Ventures and selected angels.
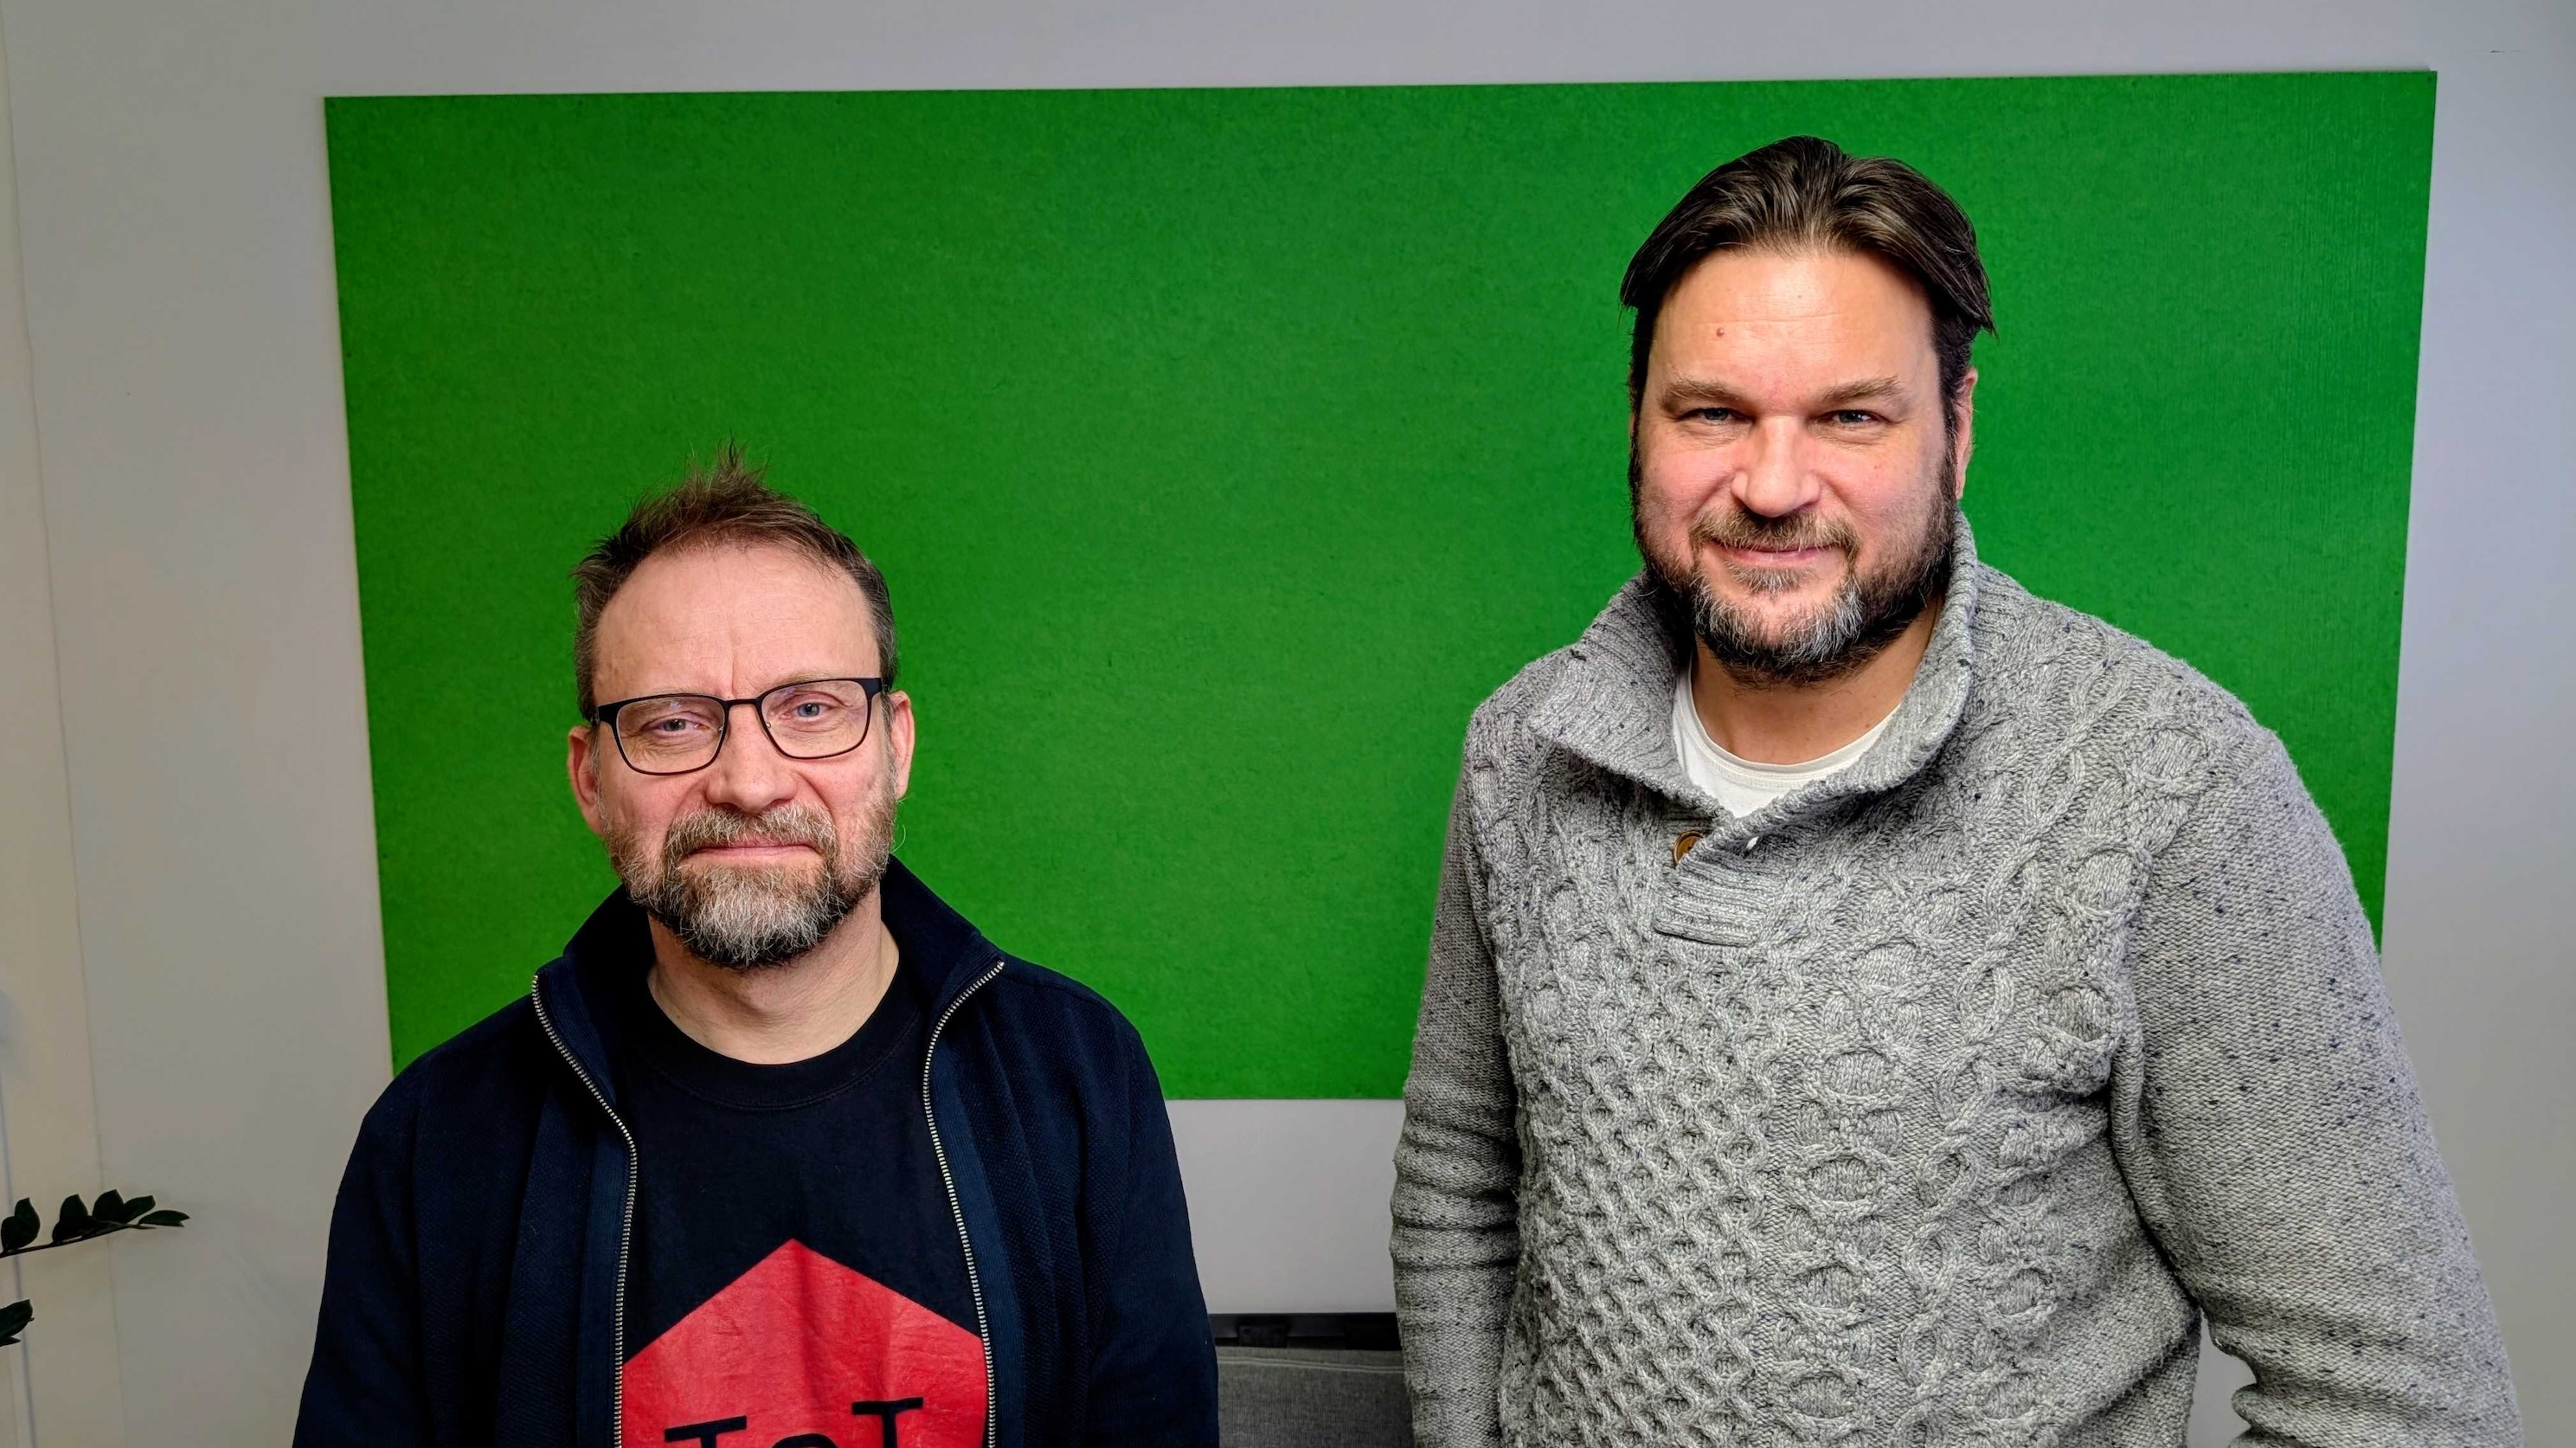
Marcus reached out to Sami Ahvenniemi, Partner at Vendep, as the round opened. Before the first meeting, Sami signed up for the service, connected his own GitHub repository and let Gardera run through it. As Sami’s repo is outdated Gardera found issues straight away. The product was early, but getting started was easy. That kind of first impression is hard to fake.
What built conviction
First, the team. Marcus, Patrik and Shehzaad have spent years as security engineers, consultants and AppSec leads, securing the kinds of environments their customers now run. On paper that is strong. In conversation it grew much deeper. “You can’t read it from a LinkedIn profile or even from the deck. Only by talking to them do you realise how skilled these guys are,” Sami says.
Second, the market. AI is changing both sides of software security at once. Attacks are becoming automated, fast and very good at finding every gap and vulnerability. Meanwhile companies are deploying agent-written code at a volume no security team can review by hand. Keeping up requires understanding the whole software delivery chain at the same time: the first line of generated code, the full pull requests, the dependencies that get pulled in, what runs in production and the cloud infrastructure underneath. Gardera covers that whole path with three products: GardHunt for code and supply chain, Cloud for cloud infrastructure, and GardStrike for AI penetration testing, on demand or continuously.
Third, early customer proof. Gardera has a number of customers running while the full platform is weeks from launch. However, this is a bet on the team, the vision and the market need more than on those customer references. What also added to the investment decision: a couple of our own portfolio companies tested the software and told us they would want it securing their applications.
“The problem was never a shortage of findings. Every team we joined already had more than it could act on. What none of them had was someone to do the work.”
Marcus Modin, co-founder and CEO of Gardera
What comes next
After launch, the product will obviously keep growing in both breadth and depth. However, for explosive growth, the hard part will be getting the onboarding to be very smooth. With a product this broad, the path from a first test to conviction to full integration has to be painless. Nailing that conversion is what the next 18 months hinge on.
That is also where we can help. Sami and Sakari Pihlava both have long histories in cybersecurity, as operators and as investors, and we plan to put that network and industry understanding to work for the team as Gardera goes after category leadership in agentic security.
Welcome to the Vendep community, Gardera! 💚